by Michael Hollister
Exclusive published at apolut media as a “Tagesdosis” on September 01, 2026
1.916 words * 10 minutes readingtime
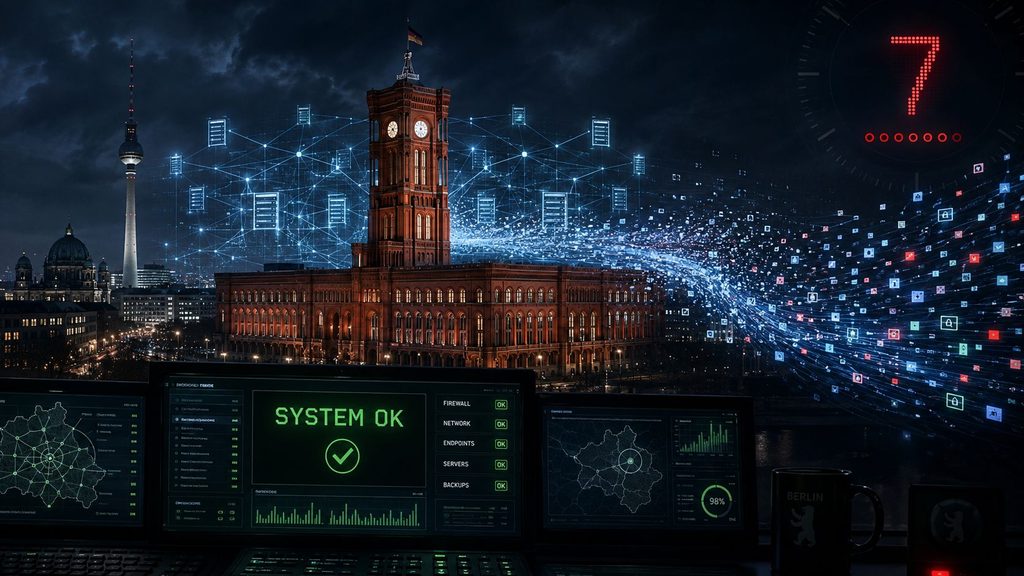
For days, attackers extracted data from the German capital’s network before anyone even noticed-and weeks later, the administration still cannot say exactly what was taken. In between came an all-clear that it was forced to withdraw shortly afterward. That is the real story worth discussing. Not the intrusion itself: Someone can penetrate a government network despite strong security measures, and such breaches occur everywhere. What matters is how quickly an attack is detected, contained, and understood. And that is precisely where the questions begin in Berlin’s case. According to the Senate, the data exfiltration took place between August 7 and August 12, 2026. It was not detected until August 14. For seven days, data left the state network without triggering a reliable alarm. The question pursued in this article is therefore not whether Berlin became a victim. It is this: Who is actually monitoring the German capital’s state network-and what does this case reveal about the gap between the state’s ambitions and its own operational performance?
The Immediate Context
On August 28, 2026, Governing Mayor Kai Wegner and Interior Senator Iris Spranger confirmed that the State of Berlin was being extorted. Their response was brief: “The State of Berlin will not be blackmailed.” The Berlin State Criminal Police Office, the public prosecutor’s office, and federal security agencies were investigating at full speed, while efforts to determine the content and scope of the exfiltrated data were continuing. Wegner and Spranger took no questions after their appearance, which lasted only a few minutes. They did not comment on the amount demanded or the identity of the perpetrators.
According to several specialist publications and the perpetrators themselves, the attack was carried out by the Rhysida ransomware group. On its leak site, the group claims to have stolen 5.79 terabytes of data comprising approximately 1.44 million files, including 46,500 contracts, emails, telephone numbers, passwords, information classified as confidential, and personal data relating to 12,076 people. The group has set a minimum auction bid of 30 bitcoin, equivalent to approximately €2 million, and imposed a deadline of about one week. So far, all these figures have come exclusively from the attackers. Berlin has confirmed neither the volume of data nor the specific claims. That also applies to the most explosive assertion: that the stolen material includes an analysis of Berlin’s water supply. Whether this is a concrete vulnerability assessment or a more general resilience study remains unclear-and as long as it does, any attempt to dramatize the claim would be irresponsible.
Rhysida is not an unknown entity. The group operates according to the double-extortion model-first stealing data, then threatening to publish it-and is listed by the monitoring service Ransomware.live as having approximately 280 victims, including the Stuttgart city administration in May 2026. Whether the group also encrypted the IT systems is secondary to this business model: Even an organization capable of restoring its systems from backups remains exposed to the threat of publication. Rhysida itself provided indications that it does possess stolen material. As evidence, it published document excerpts on the dark web bearing letterheads from entities including Berlin’s transport administration and the Bundesrat, Germany’s Federal Council.
Seven Days-and the Withdrawn All-Clear
The attack appears to have been discovered by chance. The Berlin IT Service Center noticed unusual activity on the network and raised the alarm, after which forensic investigations began. On August 14, the administration disconnected both the Senate Department for Urban Development, Building and Housing and the Senate Department for Mobility, Transport, Climate Action and the Environment from the state network. Hundreds of government locations across the capital are connected through this network. As a result, the processing of housing-benefit applications, among other services, was disrupted for days. Because the exfiltration had already ended by that point, disconnecting the departments may have limited further damage-but it could no longer reverse the loss of data. Initially, the Senate provided little public information, citing “investigative considerations”.
What followed is the heart of the matter. On August 19, Wegner told journalists that, according to the information available at the time, no sensitive data had been exfiltrated. He added a qualification: “That is the current state of our knowledge.” Initially, officials spoke only of geospatial data that was publicly available anyway. Just over a week later, the Senate Chancellery reversed that interpretation: It could “not be ruled out that personal or other nonpublic data may also have been affected”. On August 28, officials added that further data had been exfiltrated from the transport department.
The incident recalls a case previously discussed elsewhere: the European Commission, which was breached twice within two months in the spring of 2026-the very institution that prescribes security rules for an entire continent. The pattern is the same: a gap between what an institution represents to the outside world and what its operations deliver when put to the test. Berlin is therefore not an isolated case. The Stuttgart city administration was attacked in May, and an IT outage had already brought much of Berlin’s judicial system to a standstill in July. The accumulation of such incidents across the public sector is impossible to overlook.
What a Properly Monitored Network Should Have Done
This is where the sober perspective of an experienced practitioner becomes useful. A large, properly monitored government network has multiple layers of security: centralized logging, event correlation, network monitoring, endpoint detection, and-crucially-the monitoring of unusual outbound data flows and privileged accounts. The Federal Office for Information Security’s minimum standard for logging and detecting cyberattacks makes precisely this the foundation of effective security: Events must be logged and evaluated centrally, because only this evaluation makes ongoing or past attacks visible. Formally, the standard is binding on the federal administration, not on the individual states. Yet it is also recognized as a benchmark for the current state of the art-and a state administration must be measured against it.
Measured against that benchmark, the known sequence of events raises questions. A data exfiltration of this magnitude that continues for seven days and is then discovered not by the organization’s own detection systems but through an apparently accidental finding suggests gaps in both detection and response. Assuming the perpetrators’ figures are accurate, the decisive unanswered question is why exfiltration on this scale did not trigger a reliable warning sooner. The fact that, weeks later, it still had not been publicly established how the attackers entered the network in the first place makes reconstruction no easier. Rapid containment after discovery is one thing; early detection that prevents data from leaving the network for seven days is another. In this context, the most revealing statement in the entire affair came from Chief Digital Officer Florian Hauer, who admitted before the Interior Committee that officials had been “surprised by how large” their own IT system was.
The Communication-and the Election
That brings the second question into focus: not merely what officials failed to detect, but how they spoke about it. There is a difference between an agency saying that it has forensically examined a particular area and found nothing, and offering an all-clear despite not yet knowing the scope of an incident. Wegner issued his all-clear on August 19 even though the forensic investigation, as Hauer himself indicated several days later, was not yet capable of determining the extent of the breach. “It is too early to give an absolute all-clear,” Hauer said on August 24. Wegner’s qualification that his statement reflected the “current state of our knowledge” demonstrates a degree of caution-but an all-clear that must be withdrawn shortly afterward carries more weight than the caveat with which it was issued.
The same formula reappears in connection with the election. On September 20, 2026, Berlin will elect a new House of Representatives and its district assemblies, while also holding a referendum. Spranger stated that the systems required for the election were “not affected according to the current state of our knowledge” and that the election was technically secure. Hauer said there were “no indications of a threat to the elections”-while simultaneously being unable to explain how the perpetrators had entered the network at all. Readers must decide for themselves how reliable an all-clear can be when its factual basis remains unresolved. This does not amount to an accusation. It does, however, reveal a pattern: reassurance before the findings are in, three weeks before an election.
Why the Dataset Is More Dangerous Than the Headline
Public attention has focused on the number of terabytes. More revealing is what such a dataset contains. Internal emails are valuable less because of any individual message than because they form a map: They expose responsibilities, workflows, suppliers, projects, and points of contact-material that can make future deception and social-engineering attacks considerably more convincing. A collection of 46,500 contracts provides a panoramic view of service providers, maintenance agreements, security companies, and technical systems. And the real explosive charge lies in access credentials: If the breach affected not only user passwords but also plaintext credentials for service accounts, APIs, and technical accounts, simply resetting passwords will not solve the problem. Replacing such credentials throughout an entire state network is vastly more difficult. According to reports, the excerpts published by the group even included a file containing passwords in plaintext-a particularly uncomfortable discovery for an administration of this size. If personnel, judicial, or health records were also included, the consequences could extend to the personal compromise of those affected, including identity theft.
There is also the question of who now has access. The U.S. company CrowdStrike was commissioned to assist with the investigation-an understandable decision, because an incident of this magnitude immediately requires large numbers of highly specialized personnel who are scarcely available in Germany at short notice. Yet a U.S. service provider is subject to U.S. law, including the CLOUD Act, which can compel the disclosure of data regardless of where it is stored. What access rights CrowdStrike has within the state network, what data it may inspect or export, where that data is stored, and how it will be deleted or returned after the operation-these are not secondary questions. They are matters of governance that an administration must clarify in advance instead of trying to resolve them under time pressure.
What Remains
Much of the response worked as intended: The affected departments were disconnected from the network, the Berlin State Criminal Police Office, the public prosecutor’s office, and the Federal Office for Information Security were brought in, and the ransom demand was rejected-a position supported by sound security considerations. Ransomware can strike anyone today; for years, the Federal Office for Information Security has identified it as the greatest threat facing government agencies and businesses. The finding, therefore, does not lie in Berlin having become a victim.
It lies in the gap: between seven days of undetected data exfiltration and the standard of resilience that a capital city should demand of itself; between the all-clear of August 19 and its quiet withdrawal; between the reassurance offered to the public and the admission that officials were surprised by the size of their own system. An administration that loses data for days and still does not know weeks later what was stolen has less of an information problem than a control problem. For the citizens whose contracts, administrative files, and possibly personal data are contained in the stolen material, the risk has consequently shifted into a future that can no longer be contained: Unlike a password, a dataset that has already been exfiltrated cannot be rolled back. Berlin’s real test therefore still lies ahead-not in how it deals with the extortionists, but in how it answers one simple question: Who is monitoring the German capital’s state network, and what ultimately matters more-the visible crisis communication or the invisible resilience that reveals itself only when a crisis occurs?
Exclusive published at apolut media as a “Tagesdosis” on September 01, 2026
No advertisers, no sponsors, no political patrons – this publication is funded by its readers. Support independent geopolitical analysis from $5 per month and unlock all member-only content.

You are also welcome to support my work with a one-time donation.

About the Author
Michael Hollister
is a geopolitical analyst and investigative journalist. He served six years in the German military, including peacekeeping deployments in the Balkans (SFOR, KFOR), followed by 14 years in IT security management. His analysis draws on primary sources to examine European militarization, Western intervention policy, and shifting power dynamics across Asia. A particular focus of his work lies in Southeast Asia, where he investigates strategic dependencies, spheres of influence, and security architectures. Hollister combines operational insider perspective with uncompromising systemic critique – beyond opinion journalism. His work appears on his bilingual website (German/English) www.michael-hollister.com and in investigative outlets across the German-speaking world and the Anglosphere.
Fewer headlines, more context: once a week, the developments that truly matter in geopolitics.
Sources
Official Sources and Government Agencies
- The Governing Mayor of Berlin, press release of August 28, 2026, “The State of Berlin Will Not Be Blackmailed”
- Federal Office for Information Security, Minimum Standard for Logging and Detecting Cyberattacks under Section 8(1) of the BSI Act
- rbb24, “Berlin Election 2026”-House of Representatives, District Assemblies, and Referendum on September 20, 2026
Timeline, All-Clear, and Retraction
- Berliner Zeitung, “Cyberattack on Berlin Authorities: Was Sensitive Data Exfiltrated?”-Wegner, August 19, 2026
- Tagesspiegel, “No Reliable Findings: Berlin Senate Remains in the Dark After Cyberattack”-Hauer before the Interior Committee, August 24, 2026; paywalled but accessible in a browser
- Heise Online, “Sensitive Data May Have Been Affected After All in Cyberattack”
- eGovernment, “Senate Chancellery Declines to Comment on Extortionists”
Extortion, CrowdStrike, and the Volume of Data
- Tagesspiegel, “Berlin Senate Confirms Extortion: Wegner Rejects Hackers’ Ultimatum”-Commissioning of CrowdStrike
- KES Information Security, “Cyberattack on Berlin: Rhysida Claims Theft of 5.79 Terabytes”
- Born’s IT and Windows Blog, “Rhysida Cyberattackers Extort Berlin After Breaching the State Network”
Background and Precedent
© Michael Hollister – All rights reserved. Redistribution, publication or reuse of this text requires express written permission from the author. For licensing inquiries, please contact the author via www.michael-hollister.com.