by Michael Hollister
Exclusive published at Michael Hollister on November 04, 2026
4.468 words * 24 minutes readingtime
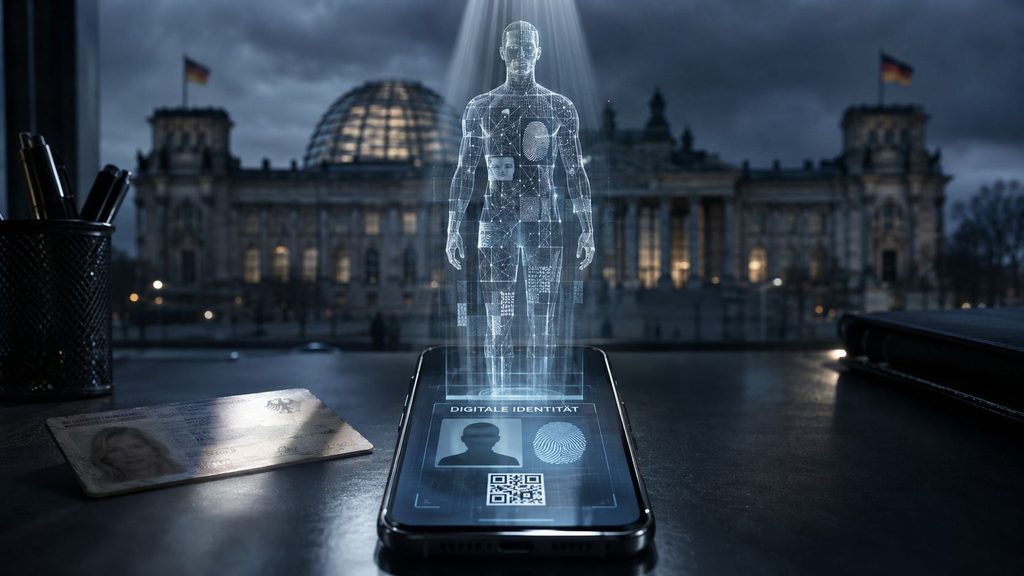
On January 02, 2027, the Federal Republic of Germany will provide its citizens with an app intended to become their “digital self.” It is called d-you, it bears the European EUDI Wallet label, and it does not meet the definition printed on it. The one protective feature that European law makes mandatory will be absent at launch. It is therefore not a certified EUDI Wallet. Germany’s Federal Office for Information Security could not certify it in this condition. And that is why this article begins not with a suspicion but with a dilemma from which the German state has no clean escape. Either d-you is an EUDI Wallet within the meaning of the regulation – in which case it must have a pseudonym function and be certified, neither of which is true, making its launch a violation of European law. Or d-you is not a completed EUDI Wallet at all, but an unfinished preliminary product – in which case Germany will miss the European deadline requiring the provision of “at least one” EUDI Wallet by the end of December 2026, because something that is not yet a fully functional wallet under Germany’s own law fulfills that obligation in name only. Both doors lead to a conflict with EU law: one through the missing protective function, the other through the missed deadline. Germany is clearly choosing the second door, and it has written the key for itself. Section 1(3) of the German implementing law expressly applies its rules to an identification mechanism that lacks the full functionality of a wallet. This provision makes the unfinished launch permissible under national law – it does not cure the conflict with European law; it merely shifts it from one obligation to the other. It is legal sleight of hand, and it raises the question posed by the entire launch: Why must a product that is neither one thing nor the other be brought to market right now, at all costs?
This is not an accident. It is a decision. And decisions have reasons.
The Bundestag adopted the underlying law on October 15, 2026, with the votes of the CDU/CSU and SPD and against the votes of the AfD, Greens, and The Left. One day earlier, the Committee on Digital Affairs had amended the government’s draft. After months of dispute over its name, the app was ultimately christened d-you and is intended to launch with approximately 40 partners from business, academia, and government that will provide their own applications. The federal government estimates one-time costs to the private sector of €13.5 million and recurring annual costs of €1.1 million, while public administration is expected to save €121.7 million each year. The total project budget for 2023 through 2028 is approximately €214 million. In both numbers and ambition, this is not a peripheral project. The Bundestag’s decision and the announced January 02, 2027, launch establish the timetable.
The question driving this article is not whether the wallet will be convenient. It will be. The question is different, and technical rather than moral: Can an identity infrastructure technically prevent abuse by a future government – or does it rely on future governments choosing not to abuse it? Anyone who builds a tool does not decide how it will be used. The builder decides only what it is capable of doing. What this tool can do is set out in the legislation adopted by the Bundestag. It is all there. One only has to read it.
The Dilemma
Let us begin with the contradiction accompanying the entire launch. The European regulation on which Germany relies – Regulation (EU) 2024/1183, commonly known as eIDAS 2.0 – does not merely require member states to provide a digital wallet. It prescribes how that wallet must be designed. Article 5a(4)(b) expressly requires the wallet to enable users to generate pseudonyms and store them locally in encrypted form. The pseudonym function is not optional. It is a legal requirement. It is the mechanism intended to prevent every interaction with an authority, every login, and every proof of age under a person’s real name from converging into a movement profile.
The reason this single function carries so much weight becomes clear when one examines the wallet’s architecture. It is not a centralized pool in which all data about everyone is stored in one place – that image would be incorrect, and supporters are right to reject it. The model is decentralized: The data resides on the user’s device. The danger lies not in a large database but in linkability. Every transaction in which a person identifies under a real name leaves a trace, and traces under the same name can be combined. The pseudonym is precisely the mechanism intended to interrupt this consolidation. It allows a person to identify themselves without providing their full name every time, turning one continuous trail into a series of separate ones. Without it, only the real name remains. And the real name connects everything.
That is exactly the function the d-you wallet will lack at launch.
Alongside this stands a second rule. Article 5c of the regulation requires the wallet to be certified – specifically, certified for compliance with the requirements laid down in Article 5a. No pseudonym function means no conformity. No conformity means no certification. This is not legal hairsplitting; it is the regulation’s basic mechanism: Something that does not meet the requirements cannot be certified, and something that is not certified is not an EUDI Wallet within the meaning of the law.
Germany knows about this dilemma. It has not overlooked it; it has factored it in. The escape route appears in the German law itself, the Act on the European Digital Identity Wallet, or EBDIG, which forms the core of the Digital Identities Act. Section 1(3) expressly applies the law’s provisions to an electronic means of identification that lacks the full functionality of a wallet. The government’s draft, Bundestag Printed Paper 21/7408, sets out both Section 1(3) and the experimental clause in Section 23. The explanatory memorandum openly states the reason: to ensure that the provisions cannot be “circumvented” when the full range of functions is “not yet” available. The only condition is that the identification function exists. In other words, the law incorporates the incomplete wallet as a normal case. It is designed to permit a launch before the product is finished.
The deliberate nature of this condition is evident not from critics, but from the majority that adopted the law. In a resolution jointly passed through the Committee on Digital Affairs by the CDU/CSU and SPD, the missing pseudonym function is described verbatim as “mandatory in order to establish compliance with directly applicable Union law.” The coalition therefore states in an official document that the function is mandatory and necessary for compliance with binding EU law – and in the same breath approves a launch without it. According to the resolution, the federal government is to provide it “if not at launch, then promptly.” Promptly is not a date. It is a promise. The committee report records the resolution on pseudonyms, the motion to delete Section 23, and the amendment limiting the duration of experiments.
There is also a second gap left by European law itself, and it explains something about the direction of the project. Zero-knowledge proof – a cryptographic method that allows a fact to be proven without revealing the underlying data, such as proving legal age without disclosing a date of birth – is regarded by many as the essential privacy technology for a data-minimizing identity system. In the regulation, it appears only in the recitals, not in the operative provisions. It is therefore not mandatory law but a recommendation. What would genuinely protect the data is optional; what makes it recordable is mandatory. One may regard this weighting as accidental. One may also regard it as revealing.
At this point, the perspective of someone who professionally audits such systems is useful. Certification under the BSI’s IT-Grundschutz framework operates differently from certification under ISO 27001. Under ISO 27001, an auditor may discuss the level of maturity. Where a measure is not yet in place but has demonstrably been planned and initiated, the declared commitment to implementation can influence the assessment – within limits, good intentions count. That is not how BSI IT-Grundschutz works. If a required condition is absent, the audit stops at that point. There is no “work in progress.” A requirement is either fulfilled or it is not. Anyone who has ever sat on the other side of such an audit knows that this is not negotiable. The condition exists, or it does not. The BSI describes IT-Grundschutz as its framework for information-security standards and certification.
A product intended to bundle a person’s most sensitive data – identity card, driver’s license, and, prospectively, health and payment credentials – is therefore entering production in a condition in which the responsible national security authority could not approve it under its own standards. The fact that the same authority, the BSI, is also designated as the national supervisory and certification body for this very wallet only intensifies the contradiction. There is no need to dramatize this gap. One need only ask the question that every security officer would ask: How resilient is a central identity repository that has not yet passed its own security audit against the day someone attempts to empty it? This is not a theoretical question. German government networks have been plundered in recent months on a scale that makes the answer uncomfortable – but that belongs in Part 2, where the architecture will be examined.
The Provision Allowed to Bend the Law
One provision in this law reaches farther than all the others, yet has received almost no attention in public debate. It is Section 23 EBDIG, titled “Experimental Clause; Evaluation.” Its first subsection states its purpose with a clarity that deserves to be read twice: The provision serves “to test deviations from this Act.” A law that adopts its own deviation at the same time.
The decisive shift lies in who decides on these deviations. Not the Bundestag that enacted the law, but the Federal Ministry for Digital Transformation and Government Modernization, acting with “due discretion,” with effect through publication in the Federal Gazette. The ministry does not need to submit an amending law to parliament for an approved deviation. It uses the latitude parliament granted it in advance. More precisely, the Bundestag’s Committee on Digital Affairs secured a right to participate: It must be informed before publication and receives at least 2 sitting weeks to submit a statement. A statement is not consent. The ministry must take note of it, not follow it.
What may be tested is set out in a list of 11 items, several of them consequential. Item 2 permits the automation of decisions about the validity or effectiveness of a wallet, expressly “including AI.” Item 3 permits automated decisions about personal identification data themselves. Item 4 opens new forms of cooperation among passport, identity-card, resident-registration, and wallet authorities, including joint blocking procedures. Item 8 permits the connection of previously separate processes and administrative procedures. The list identifies biometric procedures as a permissible field of experimentation. And item 10 permits personal identification data to be issued to minors from the age of 13 and allows identity verification to be transferred to “suitable private third parties.” A 13-year-old is regarded as too young for a social network; apparently not for the official issuance of a digital identity.
It is worth pausing to consider what this means in combination. The law creates a legal space in which software may decide automatically, if necessary using artificial intelligence, whether a person’s digital identity is valid at that moment; in which previously separate registers and procedures may be connected; in which biometric processes may be tested; and in which identity verification may be transferred to private companies – the explanatory memorandum names banks, postal services, and pharmacies as examples. Anyone asking which private entities worldwide have the greatest experience collecting and exploiting identity data can answer the question of the most likely candidates without assistance.
Anyone wishing to understand what this can mean in practice need not speculate; one can look to China. In Henan Province in June 2022, authorities turned the health codes of bank customers red – people who wanted to protest and recover their frozen savings. In China’s pandemic system, a red code meant no access to public places, trains, or buses. Affected residents told the Associated Press that their codes turned red after contact with police despite negative COVID tests. One man’s code turned red at Zhengzhou railway station, after which he was taken into police custody; hours after authorities removed him from the city, the code turned green again. This had nothing to do with infection. It had everything to do with control. That is the difference between a system that grants access and one that decides access.
Section 23 does provide a right to review automated decisions, and the General Data Protection Regulation continues to apply. That is the fair counterargument, and it belongs here. But it addresses the wrong point in time. A subsequent review does not help a citizen at the moment the identity is needed and fails – at a counter, at a border, or in front of a locked government portal. Anyone who has tried to correct an automated error and could not reach a human being capable of reviewing it knows the powerlessness behind the process. The right to object later does not replace an identity that must work now.
The record of the parliamentary deliberations shows that this provision worries more than critics outside parliament. The Left parliamentary group moved to delete Section 23 in its entirety. Its reasoning focused on the separation of powers: The clause would allow the executive branch to deviate from parliamentary laws for years without even naming each affected provision individually. The motion was rejected – and the composition of that rejection is noteworthy. The CDU/CSU, SPD, and AfD voted together against deletion; the Greens abstained. On the question of whether a ministry should receive a statutory blank check to deviate from parliamentary legislation, the governing coalition found the AfD at its side.
One detail of the oversight arrangements, specifically identified by the opposition, is especially revealing: Section 23 does not generally require Bundesrat approval for individual experimental decisions – although elsewhere, for ordinary statutory instruments, the law expressly requires the Bundesrat’s consent. The Left pointed out that the ministry might therefore even be able to deviate from rules whose original enactment would have required approval by the chamber representing Germany’s states. The deviation thus bypasses an oversight mechanism provided for ordinary cases. Anyone who creates such an instrument does not create it to leave it in the cabinet.

Parliament did at least introduce one limit. The original government draft of July 29 allowed such experiments to be repeatedly extended without expressly limiting the number of extensions. In the version amended and adopted on October 14, only one additional fixed term is permitted – turning 2 years into no more than 4. This reassurance is real. But it extends only as far as the law remains unchanged. One extension option is already built in; a second would require only another statutory amendment. Anyone seeking to guarantee today that 4 years will not become 6 or 8 would have to vouch for the intentions of every future parliamentary majority. No one can provide that guarantee. A government does not voluntarily relinquish a tool that proves useful during an experimental period; it is more likely to amend the law standing in its way. This is not an insinuation but the sober experience of temporary powers – one need only recall how many emergency rules from the pandemic years remain in force today.
Voluntary, Until Further Notice
One word hangs over this entire project as reassurance, and it even appears in the law. Article 5a(15) of the European regulation states it unambiguously: “The use of European Digital Identity Wallets shall be voluntary.” Anyone who does not use one may not be “restricted or disadvantaged in any way” when accessing public or private services. Other means of identification must remain available. That is the promise. The question is not whether it applies today. The question is how long it will apply and what it will be worth if circumstances change.
Voluntary use is guaranteed by law, and laws can be amended. Recent events have demonstrated more than once how easily, and through which procedures, that can happen. It does not even require a majority openly voting against citizens; the right timing and an exploited procedural rule are enough. No one can guarantee that voluntary use will survive the next legislative term. It is not embedded in the technology. It depends on political will, which changes with every election. A government with different intentions would not even need to ban or force the wallet; it would only need to delete the one sentence that currently says “voluntary.”
But voluntary use can remain fully enshrined in law and still disappear. That is the subtler and more likely route, and it operates through mandatory acceptance. Article 5f of the regulation requires private entities to accept the wallet when they are already required by law, contract, or regulatory obligation to use strong user authentication. The regulation itself lists the sectors concerned, and the list reads like a cross-section of daily life: transport, energy, banking, financial services, social security, health, drinking water, postal services, digital infrastructure, education, and telecommunications. The acceptance requirement takes effect no later than 36 months after the implementing acts enter into force – meaning by the end of 2027. Very large online platforms will also have to offer the wallet as a login option. A detailed FAQ on the EUDI Wallet describes its intended fields of use and the surrounding legal framework.
Consider an airport. Today, a person identifies themselves with a paper passport, and the airline must accept it. Once a requirement to accept the digital wallet exists, will there still be a corresponding requirement to accept the physical passport? Or will the operator discover that digital processing is faster, cheaper, and more convenient, allowing the analog route to wither until it exists only on paper? The 2 sets of lanes are easy to imagine: 9 lanes that process the wallet within seconds, and a tenth where anyone insisting on paper must wait while documents are handled manually. No one has abolished choice. It has merely been made so costly that hardly anyone still chooses it. The regulation does require other means to remain available, and Article 5a(15) prohibits discrimination against anyone avoiding the wallet – that is the counterargument, and it must be taken seriously. But voluntary use will not be decided by the regulation’s wording; it will be decided by the practices built around it. And practice already knows how to hollow out voluntariness.
One need only look across the border to Austria, where the state electronic identity, ID Austria, carries the same promise: voluntary use. Parliamentary inquiries document that farmers have come under pressure to use ID Austria if they want access to subsidies. In the spring of 2025, the Sokrates school administration system linked access to multifactor authentication through ID Austria; since then, federal teachers have had to enter grades through that route. A teacher in Vienna who refused to use ID Austria received an official instruction to enter her grades through that very system. She continued to refuse and was dismissed without notice.
The case should be presented fairly: She disobeyed an official instruction, which is the allegation on which the dismissal rests. The honest question is what that instruction required. It required her to use something whose use is voluntary under the law. The responsible ministry identified 2 alternatives – logins through private providers such as Microsoft or Google, or a FIDO2 security key. But the FIDO2 route also requires ID Austria, while the other 2 options mean transferring the identity data of teachers and students to American corporations. The union calls the mechanism by the only accurate term: “indirect compulsion.” No one is required to possess ID Austria – but anyone who can perform their official duties only through it no longer has a choice but an instruction. Voluntary use is not abolished. It is hollowed out until only the word remains. An Austrian parliamentary inquiry documents ID Austria as a decisive condition for federal teachers. According to a separate parliamentary inquiry on pressure involving farmers and compulsory use, a government representative publicly stated as recently as June 2025 that there would be no compulsory use of ID Austria before 2029 – while, at the same time, someone had already lost her job for refusing it.
Germany already knows this mechanism, and in an area involving more than subsidies and grades – it involves one’s own body. The Organ Donation Register has existed since March 18, 2024. Anyone wishing to record a declaration there – consent or, crucially, refusal – can do so only after electronic identification: either through the online identity function of the national identity card, together with a 6-digit PIN, an NFC-enabled smartphone, and the official identity-card app, or through the health insurer’s HealthID. The official explanation of the Organ Donation Register describes these digital access requirements. The process provides no way to register or object on paper; the paper organ donor card is a separate, legally weaker document and does not replace an entry in the register. The minimum age for using it is 16.
This means that anyone who avoids digital identification as a matter of principle cannot record their wishes in the central state institution created for that purpose. Participation is voluntary. But the only door through which a person can exercise the right leads through the system they did not want to use. This carries more weight than the cases involving farmers or the teacher because it concerns neither a subsidy nor a job, but the most personal decision about what happens to one’s body after death. Anyone wishing to make and officially record that decision must use digital identity. It is the same pattern, only closer to the skin: Digital identification is not mandatory. It is merely the only route.
This is the mechanism at issue, and it can be summarized in one sentence. Voluntary use that depends on a single statutory provision, a procedural change, or the silent elimination of an analog alternative is not a property of the system. It is a setting that can be changed. The decisive question is therefore not whether the wallet is voluntary today – it is. The question is what will prevent the state from turning the offer into a condition tomorrow. Based on everything the documented precedents show, the honest answer is: nothing except its own will.
Why the Rush?
Taken together, the result is a peculiar picture. A product without the mandatory protective function. A security audit it would not pass. An experimental clause allowing the executive branch to deviate from parliamentary legislation for 4 years and make automated decisions about the validity of an identity. And voluntary use that lasts only as long as the political will supporting it. None of these features is an accident. Each appears in the law because someone wanted it there.
That leaves the question encompassing all of this, which this first part deliberately leaves open: Why is a state pushing such a system through – late, because the European deadline expired in December 2026; legally unfinished; against warnings from its own data-protection officials and experts – and why right now, on January 02? Anyone who accepts a design flaw of this magnitude must have a reason that outweighs the flaw. That reason is not found in the d-you app. It is found in what is intended to be built on top of it.
That is the subject of Part 2.
About the Author
Michael Hollister
is a geopolitical analyst and investigative journalist. He served six years in the German military, including peacekeeping deployments in the Balkans (SFOR, KFOR), followed by 14 years in IT security management. His analysis draws on primary sources to examine European militarization, Western intervention policy, and shifting power dynamics across Asia. A particular focus of his work lies in Southeast Asia, where he investigates strategic dependencies, spheres of influence, and security architectures. Hollister combines operational insider perspective with uncompromising systemic critique – beyond opinion journalism. His work appears on his bilingual website (German/English) www.michael-hollister.com and in investigative outlets across the German-speaking world and the Anglosphere.
Stay informed without having to work through the daily flood of news – the most important developments and connections summarized for you.
Sources
EU Legal Framework
- Regulation (EU) 2024/1183 (eIDAS 2.0), consolidated version of Regulation 910/2014 as of October 18, 2024 – Article 5a(4)(b), pseudonym function; Article 5a(15), voluntary use; Article 5c, certification; Article 5f, mandatory acceptance: https://eur-lex.europa.eu/eli/reg/2014/910/2024-10-18/deu/pdf
German Legislation (Digital Identities Act / EBDIG)
- Bundestag Printed Paper 21/7408 – Government draft of the Digital Identities Act and text of the EBDIG, Sections 1(3) and 23: https://dserver.bundestag.de/btd/21/074/2107408.pdf
- Bundestag Printed Paper 21/8617 – Recommendation and report of the Committee on Digital Affairs, including the resolution on the pseudonym function, the motion to delete Section 23, and the amendment limiting the duration of experiments: https://dserver.bundestag.de/btd/21/086/2108617.pdf
- EUDI Wallet d-you: Bundestag approves launch on January 02, 2027 (Wortfilter.de, October 17, 2026): https://wortfilter.de/eudi-wallet-d-you-bundestag-start-2027/
- FAQ on the EUDI Wallet (Netzpolitik.org, Daniel Leisegang): https://netzpolitik.org/2026/faq-zur-eudi-wallet-die-wichtigsten-fragen-und-antworten-zur-digitalen-brieftasche/
Certification / BSI
- Federal Office for Information Security, IT-Grundschutz: https://www.bsi.bund.de/DE/Themen/Unternehmen-und-Organisationen/Standards-und-Zertifizierung/IT-Grundschutz/it-grundschutz_node.html
Austria / ID Austria
- Vienna teacher dismissed after refusing to use ID Austria (VOL.at, July 17, 2025): https://www.vol.at/wiener-lehrerin-nach-verweigerung-von-id-austria-entlassen/9557390
- Parliamentary inquiry, Austrian Parliament, 28th legislative period, J/3410, ID Austria as a decisive condition for federal teachers: https://www.parlament.gv.at/dokument/XXVIII/J/3410/fname_1721034.pdf
- Parliamentary inquiry, Austrian Parliament, 28th legislative period, J/3046, compulsory use of ID Austria, pressure on farmers over subsidies, and the government’s statement that there would be “no compulsory use before 2029”: https://www.parlament.gv.at/dokument/XXVIII/J/3046/fname_1710570.pdf
Organ Donation Register
- Organ Donation Register: How it works (Federal Institute of Public Health / organspende-info.de): https://www.organspende-info.de/organspende-register/
China / Health Code
- Residents say China used health tracker for crowd control (Associated Press via The Hill, June 2022): https://thehill.com/homenews/ap/ap-health/residents-say-china-used-health-tracker-for-crowd-control/
© Michael Hollister – Redistribution expressly encouraged.
I am pleased when my articles, commentaries, and analyses attract interest and are shared. Reproduction, distribution, and publication of my texts, in whole or in part, on other websites, blogs, or in other publications is expressly permitted and encouraged. No prior permission is required.
The sole requirement: Michael Hollister must be clearly and prominently identified by name as the author. In addition, a clearly visible, clickable link to the original website, www.michael-hollister.com, must be included.
Reuse without author attribution and a link is not permitted.
If this work helps you understand what lies behind the headlines, consider supporting it. Membership starts at $5 per month, includes access to all supporter-only analyses, and can be cancelled at any time.